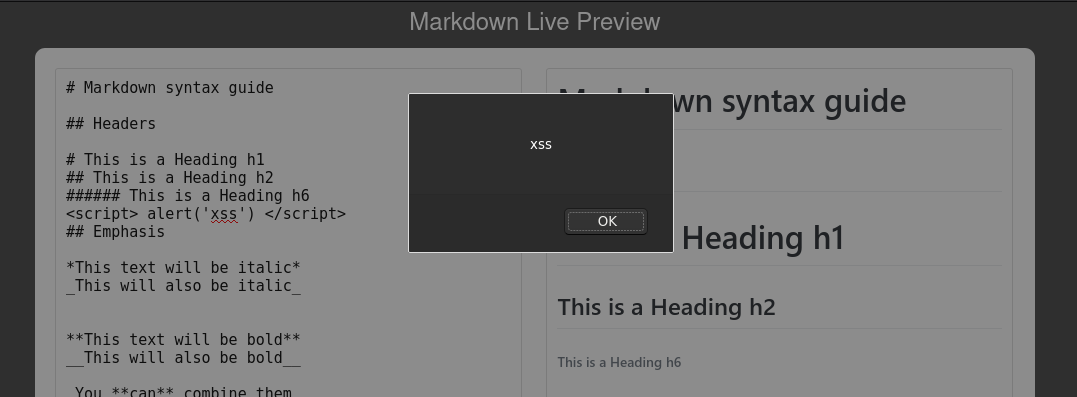
F[0x04] Reflected XSS in Markdown Live Preview
In this post I will describe a (small) vulnerability I discovered when testing the security of online markdown editors.
The specific editor in which I found this reflected XSS vulnerability was Markdown Live Preview.
The Finding
As described in this issue, the vulnerability can be exploited by entering javascript anywhere in the editor.
I could not find a way to turn this into a stored XSS attack, since the platform did not allow me to store and/or share the markdown I wrote down, a common feature in other online editors.
Remediation
Sanitizing the user-supplied markdown remediates this vulnerability, as is showcased in the applied fix.